 SimSmsBox
Quick answer: An MFA fatigue attack (also called push bombing) is when an attacker who already has your password spams you with endless “approve login?” push notifications, hoping you’ll tap “approve” out of annoyance, confusion, or just to make them stop. It exploits people, not technology. The defenses: never approve a prompt you didn’t start, use number-matching push or codes instead of one-tap approval, and know that a flood of prompts means your password is already compromised.
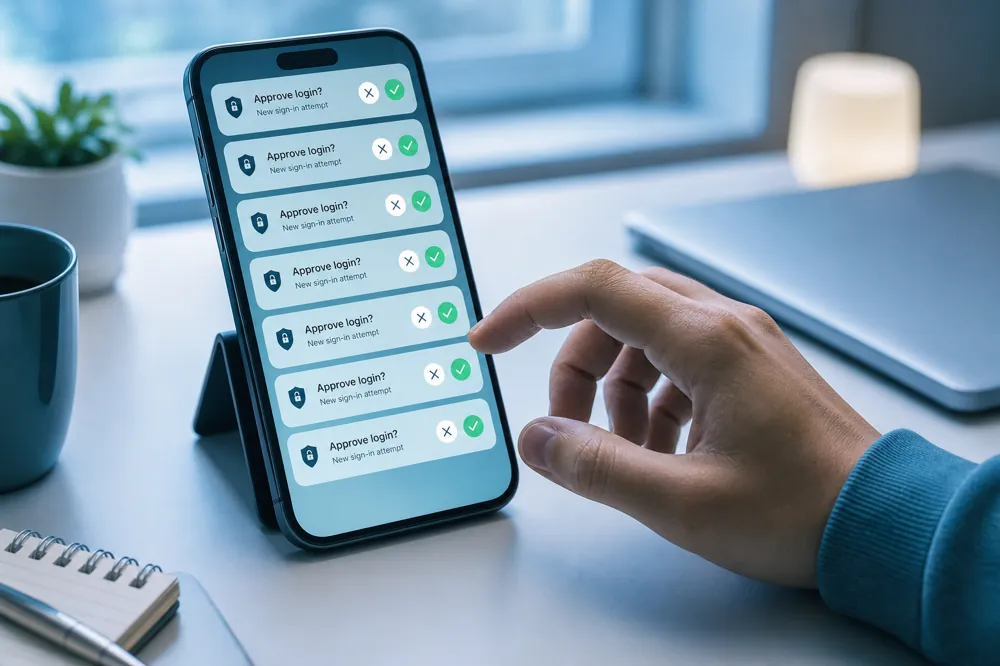
Push-based 2FA is meant to be easy: tap “yes, it’s me” and you’re in. MFA fatigue turns that convenience into the weakness. The attacker has your password and just needs one careless tap — so they send prompt after prompt until you give in. Here’s how the attack works and how to shut it down.
1. How push bombing works
The attack has a simple, ugly logic:
- The attacker already knows your password (from a breach, phishing, or credential stuffing).
- They repeatedly try to log in, which fires a push “approve?” notification to your phone each time.
- Prompts pile up — during a meeting, in the middle of the night, dozens in a row. Some campaigns pair the flood with SMS noise or a fake “IT support” call telling you to approve.
- Eventually you tap “approve” to stop the noise, or assume it’s a glitch — and they’re in.
Once approved, the attacker holds a live session and often moves fast: silencing alerts, changing the recovery email, or adding their own second factor so you can’t simply revoke them later.
The technology worked perfectly; the human got worn down. That’s why it’s called fatigue.
2. Why one-tap push is the vulnerable part
The weakness is specifically the “approve/deny” push that needs no thought. Compare the common second factors:
| Second factor | Vulnerable to fatigue? |
|---|---|
| One-tap push approval | Yes — the target of the attack |
| Number-matching push | Much less — you must enter a shown number |
| SMS / app code | No — attacker never receives the code |
| Passkey / hardware key | No — requires your device/biometric |
Notice that a code factor is immune: with SMS or an authenticator, the attacker would need the actual code, which never reaches them. Fatigue only works when approval is a reflexive tap. This is a key nuance in the push vs SMS trade-off.
3. MFA fatigue vs OTP bombing
A prompt flood and a code flood look similar on your lock screen but are different attacks with different prerequisites:
| MFA fatigue | OTP bombing | |
|---|---|---|
| Prerequisite | Password usually already known | Password not required |
| Channel | Push approval (sometimes plus SMS) | Flood of SMS codes |
| Win condition | You approve, or read a code aloud | Often harassment, or setup for social engineering |
| Defense focus | Deny unknown prompts, stronger second factor | Rate limits, never share codes |
The two can stack: SMS chaos first to create panic, then push prompts while you’re rattled. The tell that separates them is whether the prompt asks you to approve something or merely delivers digits.
4. How to defend against it
- Never approve a prompt you didn’t trigger. If a login request appears when you’re not logging in, deny it — every time.
- Treat a flood of prompts as an alarm: it means your password is already known. Change it immediately, from a device you trust, and revoke any sessions you don’t recognise.
- Switch to number-matching push or codes if your service offers them, so approval can’t be a mindless tap.
- Check what else changed. After a flood, confirm the recovery email, phone number and registered second factors are still yours — an attacker who got in once will try to keep the door open.
- Keep backup codes so you’re never forced to stay on push-only just to retain access.
- Report repeated prompts to the service or your IT team; it signals an active attack.
The mindset shift: an unexpected 2FA prompt isn’t noise to dismiss — it’s evidence someone has your password.
5. What services should build in
Fatigue is as much a product flaw as a user mistake. If you run the login flow, the countermeasures are on your side:
- Rate-limit approval requests and alert on bursts, instead of firing a push for every retry.
- Show context in the prompt — location, device, IP — so “approve?” carries enough information to answer.
- Require number matching rather than a bare approve/deny button.
- Trigger step-up checks for logins from unusual locations.
- Offer non-push factors by default, so convenience isn’t the only option on the menu.
For users, the summary is blunt: one-tap approve also one-taps the attacker in.
6. What this means if you receive codes online
MFA fatigue specifically targets push approval, not codes. If you receive codes online without a SIM, you’re using a code-based factor — the attacker never sees your code, so there’s nothing for them to spam you into approving. Code factors sidestep fatigue by design.
The broader lesson holds for any factor: only complete a verification you initiated. A code that arrives when you’re not logging in — like an unexpected push — is a red flag that your password is out there, not a prompt to act on.
FAQ
Q: What is MFA fatigue / push bombing? An attack where someone with your password floods you with push-approval requests until you tap “approve” by mistake or annoyance, granting them access.
Q: Does it work against SMS or authenticator codes? No. Fatigue relies on one-tap approval. With codes, the attacker never receives the code, so spamming prompts gets them nowhere.
Q: What should I do if I get a flood of login prompts? Deny them all, assume your password is compromised, and change it right away. Then consider switching to number-matching push or a code-based factor.
Q: I never approved anything — am I already breached? Probably not yet, but your password almost certainly is. Rotate it and audit active sessions. If you did tap approve at any point, treat the account as compromised and check for account takeover signs.
Q: Will muting notifications protect me? It reduces the chance of a mis-tap, but it fixes nothing: the stolen password is still valid and the login attempts continue silently. Change the credential and harden the second factor.
Takeaway
MFA fatigue floods you with push-approval prompts hoping you’ll tap “approve” to make them stop — an attack on your patience, not your technology. Defeat it by never approving a login you didn’t start, treating a prompt flood as proof your password leaked, and favoring code-based factors, which an attacker can never spam you into handing over.
Related reading
- What Is OTP Bombing?
- What Is Account Takeover (ATO)?
- Security Keys vs SMS 2FA
- What Are 2FA Backup Codes?